Networks are the backbone of modern organizations. Employees, servers, applications, databases, cloud services, and devices all communicate through network infrastructure.
Because networks connect so many important systems, a security weakness in a network can potentially create serious risks.
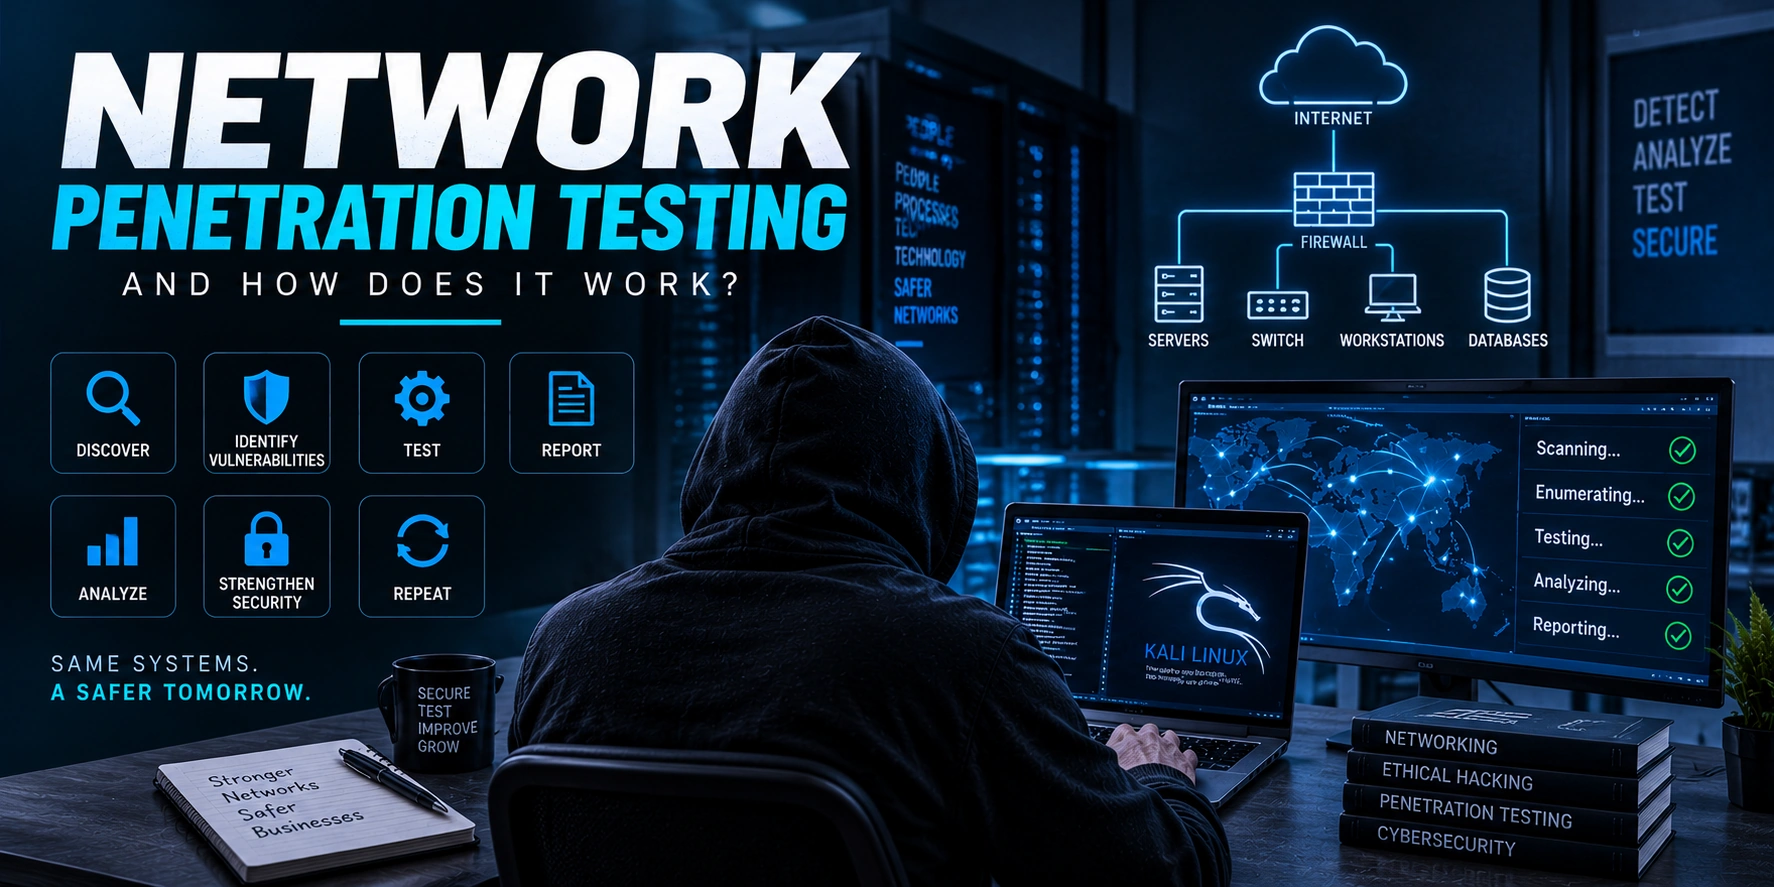
Network penetration testing helps organizations identify and understand security weaknesses in their network infrastructure through authorized and controlled security testing.
In this guide, you’ll learn what network penetration testing is, how it works, the different types of network penetration tests, what areas are commonly assessed, and why it is important for cybersecurity.
Important: Network penetration testing should only be performed with explicit authorization. Testing networks without permission can be illegal and may disrupt systems or services.
What Is Network Penetration Testing?
Network penetration testing, often called network pen testing, is an authorized security assessment designed to identify and safely validate potential security weaknesses in network infrastructure.
The goal is to understand whether weaknesses could expose an organization’s systems, services, or sensitive information to security risks.
A network penetration test may assess areas such as:
- Network devices
- Servers
- Network services
- Firewalls
- Access controls
- Internal infrastructure
- External infrastructure
- Security configurations
A simplified process looks like this:
Network Infrastructure
        ↓
Authorized Security Assessment
        ↓
Identify Potential Weaknesses
        ↓
Safely Validate Findings
        ↓
Analyze Risk
        ↓
Improve Security
The purpose is defensive: find and address weaknesses before they can be abused by malicious attackers.
How Does Network Penetration Testing Work?
A network penetration test follows a structured methodology.
The exact process depends on the organization’s environment and the agreed testing scope, but it generally includes the following stages.
1. Authorization and Scope Definition
Before testing begins, the organization and security team define exactly what is authorized.
The scope may specify:
- Networks that can be tested
- Systems included in the assessment
- Testing dates
- Allowed testing activities
- Restricted systems
- Emergency contacts
- Data handling requirements
A simple example:
Authorized Scope
├── Internal Test Network
├── Approved Servers
└── Authorized Network Devices

Out of Scope
├── Third-Party Systems
├── Personal Devices
└── Unapproved Services
Clear scope definition is essential because it prevents accidental testing of systems that are not authorized.
2. Information Gathering
Once the assessment begins, security professionals collect information about the authorized network environment.
The goal is to understand the infrastructure.
This may include information about:
- Network ranges
- Hosts
- Services
- Operating systems
- Network architecture
- Security controls
The process can be summarized as:
Authorized Network
        ↓
Understand Infrastructure
        ↓
Identify Systems
        ↓
Map Services
        ↓
Security Assessment
Information gathering helps testers understand where security risks may exist.
3. Network Discovery
The next stage involves identifying systems and services that are accessible within the authorized scope.
Security professionals may look for:
- Active systems
- Network services
- Exposed ports
- Unexpected services
- Unnecessary network exposure
For example:
Network
├── Server
│   ├── Web Service
│   └── Database Service
│
├── User Devices
│
└── Network Devices
    ├── Router
    └── Firewall
The goal is to understand the network’s attack surface.
An exposed service is not automatically a vulnerability. It must be reviewed in context.
4. Security Assessment
After understanding the network environment, testers review systems for potential security weaknesses.
Common areas may include:
Network Services
Security teams may review whether unnecessary services are exposed.
Security Configurations
Incorrect configurations can sometimes increase security risks.
Examples may involve:
- Weak access controls
- Unnecessary network exposure
- Outdated security settings
- Improper service configurations
Access Controls
Testing may review whether systems enforce appropriate authorization.
The goal is to confirm that users and systems can only access resources they are authorized to use.
System Updates
Outdated software can potentially contain known security weaknesses.
Security professionals may review patch and update management as part of the assessment.
5. Vulnerability Identification
During the assessment, security tools and manual analysis may identify potential vulnerabilities.
A typical process looks like:
Network System
       ↓
Security Review
       ↓
Potential Vulnerability
       ↓
Validation
       ↓
Confirmed Finding
Automated tools can help identify potential issues.
However, results must be reviewed carefully because automated scans may produce:
- False positives
- Informational findings
- Low-risk issues
Professional analysis is required to understand the real risk.
6. Safe Validation
After identifying a potential weakness, the security professional may safely validate it within the approved scope.
The objective is to determine:
- Whether the weakness is genuine
- Whether it creates meaningful security risk
- What systems may be affected
- What the potential business impact could be
A professional assessment avoids unnecessary disruption.
The process is:
Potential Weakness
       ↓
Controlled Validation
       ↓
Confirmed Risk
       ↓
Impact Analysis
7. Impact Analysis
A confirmed technical issue must be evaluated based on its potential impact.
Security teams may consider:
- Confidentiality risks
- Integrity risks
- Availability risks
- Business impact
- Systems affected
A simple risk model is:
Likelihood
    +
Potential Impact
    ↓
Risk Priority
This helps organizations decide which security issues should be addressed first.
8. Reporting
After testing is complete, the security team prepares a report.
A good network penetration testing report usually includes:
- Assessment scope
- Testing methodology
- Summary of findings
- Risk levels
- Affected systems
- Potential impact
- Recommended remediation
The report should help both technical teams and management understand the results.
9. Remediation and Retesting
After security issues are identified, the organization works to address them.
Possible remediation activities include:
- Updating systems
- Changing configurations
- Improving access controls
- Removing unnecessary services
- Strengthening network segmentation
- Improving monitoring
After changes are made, retesting can help verify that the identified security issue has been resolved.
Security Finding
       ↓
Remediation
       ↓
Retesting
       ↓
Verified Improvement
Types of Network Penetration Testing
Network penetration testing can be performed from different perspectives.
External Network Penetration Testing
External testing focuses on systems that are exposed to the internet or other external networks.
The purpose is to understand the organization’s external attack surface.
Common areas include:
- Internet-facing servers
- Public services
- Remote access systems
- External network infrastructure
A simplified model:
Internet
   ↓
External Services
   ↓
Security Assessment
Internal Network Penetration Testing
Internal testing focuses on the organization’s internal network environment.
This can help assess potential risks if:
- A device becomes compromised
- Unauthorized access occurs
- An internal account is misused
Internal testing can help organizations understand whether security controls such as segmentation and access restrictions are effective.
Internal Network
       ↓
Authorized Assessment
       ↓
Security Controls
       ↓
Risk Analysis
Wireless Network Penetration Testing
Wireless assessments focus on authorized Wi-Fi and wireless infrastructure.
Areas may include:
- Wireless security configuration
- Authentication controls
- Access management
- Network segmentation
Wireless testing should only be performed on authorized networks.
Network Penetration Testing vs Vulnerability Assessment
These terms are related but not identical.
Vulnerability Assessment
A vulnerability assessment focuses primarily on identifying potential security weaknesses.
Identify
   ↓
Review
   ↓
Prioritize
Network Penetration Testing
A penetration test goes further by safely validating selected findings to understand whether they create a meaningful security risk.
Identify
   ↓
Analyze
   ↓
Safely Validate
   ↓
Understand Impact
Both processes are important for cybersecurity.
Network Penetration Testing vs Ethical Hacking
Ethical hacking is a broad term for authorized security testing activities.
Network penetration testing is a specific type of security assessment focused on network infrastructure.
Ethical Hacking
      ↓
Multiple Security Areas
      ↓
Network Penetration Testing
      ├── External Testing
      ├── Internal Testing
      └── Wireless Testing
What Is Tested During a Network Penetration Test?
The exact scope depends on the organization.
Common areas may include:
- Servers
- Firewalls
- Routers
- Switches
- Network services
- Remote access systems
- Internal infrastructure
- Wireless networks
- Access controls
- Network segmentation
The goal is not to test everything without limits.
Testing should always remain within the agreed scope.
Benefits of Network Penetration Testing
1. Identifies Security Weaknesses
Testing can help discover weaknesses before they become larger security problems.
2. Validates Security Controls
Organizations can evaluate whether existing security controls work as expected.
3. Helps Prioritize Risks
Not every security issue has the same level of risk.
Penetration testing can help identify which weaknesses may require urgent attention.
4. Improves Network Visibility
Security assessments can reveal unexpected services, systems, or configurations.
5. Supports Compliance and Risk Management
Some organizations use penetration testing as part of their broader security and compliance programs.
Common Network Security Weaknesses
Network assessments may identify issues related to:
- Unnecessary exposed services
- Weak access controls
- Poor network segmentation
- Outdated software
- Configuration problems
- Weak authentication
- Insufficient monitoring
The specific findings vary significantly between organizations.
How Often Should Network Penetration Testing Be Performed?
There is no single schedule that works for every organization.
Testing frequency may depend on:
- Organization size
- Network complexity
- Regulatory requirements
- Changes to infrastructure
- Business risk
Organizations may perform testing:
- Regularly
- Before major infrastructure changes
- After significant security incidents
- When launching new services
Cybersecurity should be treated as a continuous process.
Network Penetration Testing Tools
Security professionals may use different tools depending on the assessment.
Examples include tools used for:
- Network discovery
- Traffic analysis
- Vulnerability assessment
- Security monitoring
However, tools should support a structured methodology.
A tool output alone does not automatically confirm a vulnerability.
Security professionals must analyze and validate findings.
Skills Required for Network Penetration Testing
Network penetration testers need strong technical foundations.
Important skills include:
- Networking
- Linux
- Windows
- TCP/IP
- DNS
- Network protocols
- Firewalls
- Access controls
- Vulnerability management
- Security reporting
Understanding how networks work is more important than simply memorizing security tools.
Network Penetration Testing for Beginners
Beginners should start by learning networking fundamentals.
A good learning roadmap is:
Computer Fundamentals
        ↓
Networking Basics
        ↓
TCP/IP and DNS
        ↓
Linux and Windows
        ↓
Network Security
        ↓
Cybersecurity Fundamentals
        ↓
Penetration Testing Methodology
        ↓
Practice in Authorized Labs
Practice should only take place in safe and authorized environments.
Examples include:
- Personal labs
- Virtual machines
- Intentionally vulnerable environments
- Authorized cybersecurity training platforms
Common Mistakes Beginners Make
1. Focusing Only on Tools
Tools are helpful, but understanding networking is essential.
2. Testing Without Permission
Never test networks without authorization.
3. Trusting Automated Results Completely
Automated findings require validation.
4. Ignoring Network Fundamentals
Without understanding protocols and network architecture, it is difficult to understand security findings.
5. Skipping Reporting Skills
Finding an issue is only part of the job.
Security professionals must clearly explain:
- The issue
- The impact
- The risk
- The recommended solution
Frequently Asked Questions
What Is Network Penetration Testing?
Network penetration testing is an authorized security assessment that identifies and safely validates potential security weaknesses in network infrastructure.
What Is the Difference Between Internal and External Network Penetration Testing?
External testing focuses on authorized systems accessible from outside the organization, while internal testing assesses authorized systems within the internal network environment.
Is Network Penetration Testing Legal?
Yes, when performed with explicit authorization.
Testing systems without permission can be illegal.
What Skills Are Needed for Network Penetration Testing?
Important skills include networking, Linux, Windows, TCP/IP, DNS, network security, vulnerability management, and security assessment methodology.
Final Thoughts
Network penetration testing is an important part of a strong cybersecurity strategy.
It helps organizations understand whether weaknesses in their network infrastructure could create meaningful security risks.
A professional network penetration test typically involves:
- Authorization
- Scope definition
- Information gathering
- Network discovery
- Security assessment
- Vulnerability identification
- Safe validation
- Impact analysis
- Reporting
- Remediation and retesting
The goal is not simply to find technical issues.
The goal is to help organizations understand risk and improve their security.
Conclusion
Network penetration testing is a structured and authorized process used to assess the security of network infrastructure.
Security professionals examine the approved environment, identify potential weaknesses, safely validate important findings, analyze the potential impact, and provide recommendations for improving security.
For beginners, the best place to start is with networking fundamentals.
Understanding IP addresses, ports, protocols, DNS, routing, firewalls, and access controls will make network security concepts much easier to understand.
Remember:
Network penetration testing is not about attacking random networks. It is an authorized security process designed to identify weaknesses and help organizations build stronger, more secure infrastructure.